
Table of Contents
Ask a cloud provider where your data lives and you will get a precise answer: Frankfurt, Warsaw, Amsterdam. Ask which governments may be able to compel access to it and the answer is often less precise. The first question is about data residency. The second is about data sovereignty. They are easy to confuse, and the gap between them matters most for the copies organisations often think about least: backups.
Backups hold everything: databases, mailbox exports, file versions and other business-critical information, often retained for years. They may also be managed by third parties, replicated to another site or sent to a cloud storage tier. If data protection arrangements overlook jurisdiction or access risks, backup infrastructure can become an important blind spot.
Short answer: data residency describes where data is physically stored. Data sovereignty concerns the legal frameworks that apply to data and the entities that control or process it. Data localization refers to legal requirements that certain categories of data must remain within a specific jurisdiction. Storing backups in an EU data centre establishes data residency, but does not by itself determine which laws may apply to the organisations operating the infrastructure or who may have access to the data.
This article explains these concepts and the regulations relevant to IT teams. It is not legal advice.
Residency, sovereignty and localization
The three terms answer three different questions. Contracts and marketing often blur them, but they describe different aspects of data governance.
| Data residency | Data sovereignty | Data localization | |
|---|---|---|---|
| The question it answers | Where is the data stored? | Which legal frameworks apply, and which entities may control or access the data? | Must the data stay in a specific country by law? |
| What determines it | Physical location of storage and replicas | Applicable law, the entities controlling or processing the data, access arrangements and relevant jurisdictions | A specific national or sector-specific legal requirement |
| Typical evidence | Data centre region specified in a contract | Vendor ownership, jurisdiction, control-plane location, access arrangements and contractual terms | Legal text identifying the data category and localization requirement |
| Can a contract alone deliver it? | Often, if storage locations and replication are contractually restricted and verified | No. A contract cannot override applicable law or eliminate all jurisdictional exposure | No. It is determined by law |
| Example | Backups stored in an EU region | Backups stored in the EU, with the provider’s legal jurisdiction, operational access and control arrangements also assessed | Certain public-sector or sector-specific data required by law to remain in one country |
Residency describes a property of storage. Sovereignty is broader: it requires looking at the applicable legal framework, the organisations that control or process the data, the people who can access it and the technical arrangements governing access and disclosure.
Why location alone is not enough
One of the clearest examples of residency without full jurisdictional control is the relationship between US and EU rules on government access to data.
- The US CLOUD Act (2018) clarifies that providers of electronic communication or remote computing services subject to the relevant US legal obligations may be required to preserve or disclose data in their possession, custody or control, regardless of whether that data is located inside or outside the United States. The relevant provision is 18 U.S.C. § 2713.
- GDPR Article 48 limits the recognition or enforcement in the EU of third-country court judgments and administrative decisions requiring the transfer or disclosure of personal data, unless they are based on an applicable international agreement, such as a mutual legal assistance treaty.
These provisions address different legal questions. A provider subject to US legal obligations may face a disclosure request concerning data stored in Europe. At the same time, GDPR requirements continue to apply where personal data is involved. Article 48 does not automatically make every foreign disclosure request unlawful, nor does it remove the need to assess the applicable rules under GDPR Chapter V.
Moving data to an EU region therefore does not, by itself, resolve every question about jurisdiction or access. Organisations should also assess who operates the service, which entities control the data, where administrative access takes place and how access requests are handled.
We cover the legal and technical aspects of backup sovereignty in more depth on our Data Sovereignty and Compliant Backup page.
What EU rules expect from backup copies
None of the main EU frameworks establishes a universal requirement that all backups must be stored in the EU. However, several regulations impose requirements that make backup location, access, recovery and supplier arrangements important considerations.
| Regulation | What it says that touches backups | What it means in practice |
|---|---|---|
| GDPR, Article 32 | Requires appropriate technical and organisational measures, including the ability to restore the availability of and access to personal data in a timely manner after an incident, and regular testing of security measures. | Backups are a common and important measure for meeting availability and recovery requirements. Backup copies containing personal data remain subject to GDPR. |
| GDPR, Chapter V and Article 48 | Regulates transfers of personal data to third countries. Article 48 limits the recognition or enforcement in the EU of certain third-country disclosure decisions unless they are based on an applicable international agreement. | Organisations should assess whether backup storage, support access or other processing activities involve transfers of personal data to a third country, and identify the applicable legal basis and safeguards. |
| NIS2, Article 21(2) | Requires essential and important entities within the scope of the Directive to implement appropriate and proportionate cybersecurity risk-management measures, including business continuity, backup management, disaster recovery and supply-chain security. | Organisations covered by NIS2 should assess backup providers and relevant suppliers as part of their cybersecurity and supply-chain risk-management processes. |
| DORA, Articles 11 and 12 | Requires financial entities to document ICT business continuity, backup policies, and restoration and recovery procedures. Backup and recovery procedures must be tested periodically. When restoring backup data using their own systems, financial entities must use systems physically and logically segregated from the source ICT system. | Financial entities need documented backup and recovery arrangements, periodic testing and appropriate segregation to protect restoration processes. |
| EU Data Act, cloud switching | Introduces requirements designed to facilitate switching between data processing service providers and reduce vendor lock-in. It applies from 12 September 2025. Switching charges will be prohibited from 12 January 2027. | Organisations should assess contractual switching conditions, data export capabilities and technical portability when selecting cloud and backup service providers. |
The common thread is that organisations need to understand where backup copies are stored, who can access them, which legal frameworks apply and whether recovery procedures actually work. “In an EU region” answers only the first question.
Where backups break sovereignty
Most teams check residency once: production data and the primary backup target are both located in the EU. The gaps often appear later, in parts of the backup chain that are not always included in the data map.
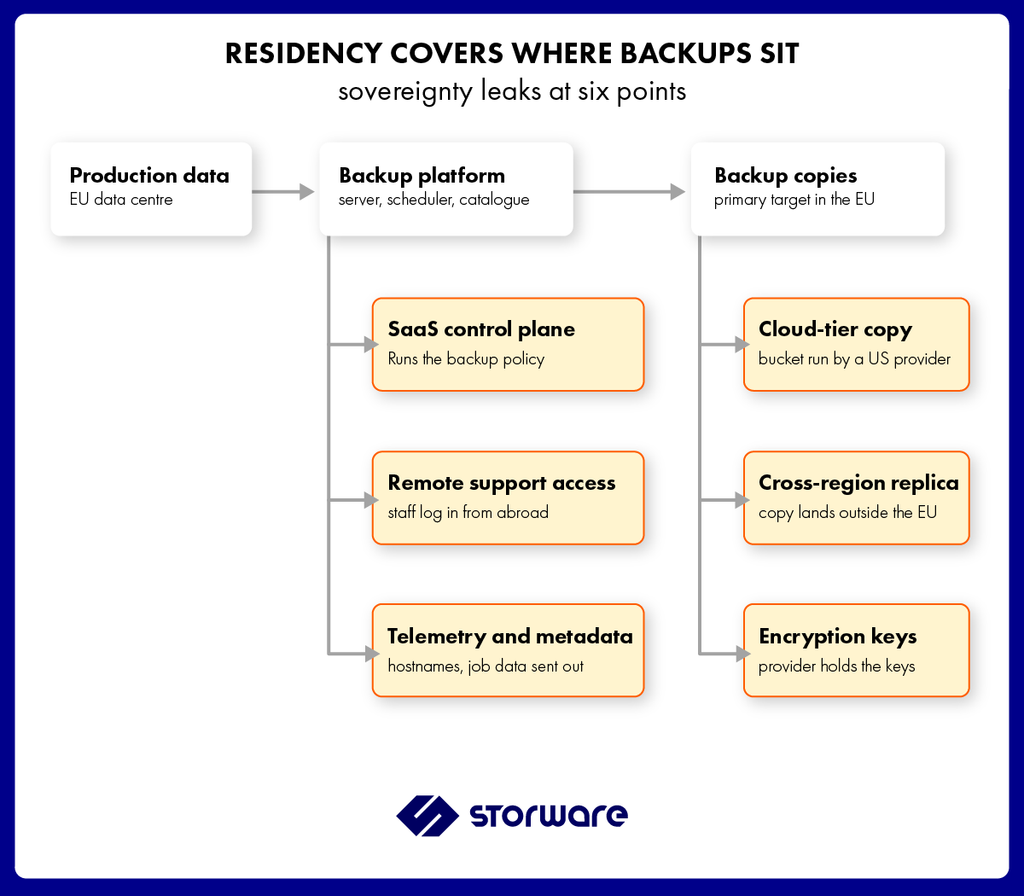
Backup chain: six areas to assess
Three areas concern the backup platform itself:
- SaaS control plane: The backup catalogue, scheduler or management interface may be hosted by a vendor in another jurisdiction.
- Remote support access: Support personnel may access systems or metadata from outside the organisation’s required jurisdiction.
- Telemetry and metadata: Hostnames, job details and operational metadata may be transmitted to the vendor or another service provider.
Three further areas concern backup copies and their protection:
- Cloud-tier copy: A secondary copy may be stored in a bucket operated by a provider subject to another jurisdiction.
- Cross-region replica: A replica may be transferred to a location outside the required jurisdiction.
- Encryption keys: The organisation may not have exclusive control over the keys used to protect its backup data. Key ownership, access rights and key-management arrangements all matter.
Each of these areas deserves assessment. Their presence does not automatically mean that data sovereignty has been compromised, but they can introduce additional jurisdictional, access or control risks even when the primary backup copy remains in the EU.
A checklist for sovereign backup
Use these questions when assessing any backup vendor or service provider. Ask for the answers in writing and retain the evidence as part of your supplier and cybersecurity risk-management process.
- Where is every backup copy stored, including secondary, cloud-tier and replica copies?
- Where does the backup control plane run, and can it run on our own infrastructure?
- Which company operates the software and support, and in which jurisdiction is it incorporated?
- Which staff can access backup data or metadata, from which countries, and is that access logged?
- Does the product send telemetry or metadata to the vendor, and can it be switched off?
- Are backups encrypted, and who manages and controls the encryption keys?
- Can at least one copy be made immutable or air-gapped under our control?
- Can we export backups in a usable form if we change vendor?
- Are backup and restore operations logged in a form an auditor can review?
The answers should cover the whole backup chain, not just the primary storage location. They should also be reviewed whenever the infrastructure, service provider or backup architecture changes.
Where Storware fits
Storware is headquartered in Warsaw, Poland, with EU-based engineering, support and control-plane operations. Storware Backup and Recovery can be deployed on infrastructure selected by the customer, who also determines where backup copies are stored — including on-premises storage, EU data centres and customer-controlled S3-compatible object storage.
This deployment flexibility helps organisations align their backup architecture with their data residency, access-control and operational requirements.
Key capabilities include:
- Immutability: Object Lock and Retention Lock help protect backup data against modification or deletion during configured retention periods. The available protection mechanisms depend on the selected storage destination and configuration. The isoLayer destination and tape can provide additional isolation for backup copies.
- Security controls: Encryption in transit and at rest, role-based access control and multi-factor authentication help protect backup data and administrative access.
- Evidence: Auditable backup and recovery records, configurable retention policies and scheduled recovery testing help organisations document their data protection and recovery processes.
Storware’s European operating structure and customer-controlled deployment options can help organisations reduce exposure to certain jurisdictional and operational risks. However, data sovereignty is determined by the complete arrangement: the customer remains responsible for assessing the applicable legal requirements, data locations, access permissions, storage providers and encryption-key management.
For more information, see Data Sovereignty and Compliant Backup.
Frequently asked questions
What is the difference between data sovereignty and data residency?
Data residency describes where data is physically stored. Data sovereignty concerns the legal frameworks that apply to data and the entities that control or process it. Data can reside in the EU while still being subject to certain foreign legal obligations if a provider or another entity controlling the data falls within the scope of another country’s laws.
What is data localization?
Data localization is a legal requirement that certain categories of data must remain within a specific country or jurisdiction. It is narrower than data sovereignty and is established by specific national or sector-specific rules.
Does storing backups in an EU data centre make them sovereign?
It establishes data residency, but it does not automatically guarantee data sovereignty. Organisations should also assess the legal jurisdiction of the entities operating the service, who can access the data, where administrative control is exercised, how encryption keys are managed and whether third-country disclosure obligations may apply.
Does the US CLOUD Act apply to data stored in Europe?
The CLOUD Act can require providers of electronic communication or remote computing services subject to the relevant US legal obligations to preserve or disclose data within their possession, custody or control, regardless of where that data is stored. Whether it applies to a particular provider and dataset depends on the legal and factual circumstances. GDPR Article 48 separately addresses the recognition and enforcement in the EU of certain third-country disclosure orders.
Are backups covered by GDPR?
Yes. Backup copies containing personal data remain subject to GDPR. Article 32 requires appropriate security measures, including the ability to restore the availability of and access to personal data in a timely manner following an incident, and regular testing of security measures.
What does NIS2 require for backups?
For essential and important entities within its scope, NIS2 requires appropriate and proportionate cybersecurity risk-management measures. These include business continuity measures such as backup management and disaster recovery, as well as supply-chain security.
How can I improve backup data sovereignty?
Assess the entire backup chain: where each copy is stored, which organisations operate the backup platform, who can access the data and metadata, how encryption keys are managed, which jurisdictions may apply, and whether you can independently restore or export your backups. Document the results and review them whenever your infrastructure or suppliers change.
Keep backups, and control over them, in Europe
Your backup strategy should protect more than the data itself. It should also give you visibility and control over where backup copies are stored, who can access them and how quickly you can recover your workloads.
Storware Backup and Recovery helps organisations protect their data across diverse infrastructures, with flexible deployment options, immutable backup capabilities and recovery tools.
Start a 60-day trial or talk to our team about sovereign backup.
Storware Backup and Recovery. #1 Backup & DR for OpenStack. Simplified. Scalable. Proven.
Legal and regulatory references
- GDPR — Regulation (EU) 2016/679, particularly Articles 32 and 48 and Chapter V.
- NIS2 — Directive (EU) 2022/2555, particularly Article 21.
- DORA — Regulation (EU) 2022/2554, particularly Articles 11 and 12.
- EU Data Act — Regulation (EU) 2023/2854.
- US CLOUD Act — 18 U.S.C. § 2713.